Deploy GreptimeDB Cluster
GreptimeDB Enterprise is released as docker images. We provide each customer with a separate private docker registry hosted on Cloud, which you can pull directly using the docker pull command or configure in helm charts.
Get GreptimeDB Enterprise
Upon receiving GreptimeDB Enterprise, you will be provided with the docker registry address, username, and password via email. Please store this information securely!
Each release of GreptimeDB Enterprise has a unique tag identifier.
With this tag, plus the registry address registry, username username, and password password provided by our staff,
you can pull the GreptimeDB Enterprise image:
- Login to docker registry:
docker login --username=<username> --password=<password> <registry> - Pull docker image:
docker pull <registry>:<tag>
Then configure GreptimeDB Enterprise in the helm chart:
First, create a pull secret for the image registry in k8s (for detailed methods and instructions, please refer to the k8s official documentation).
kubectl create secret docker-registry regcred --docker-server=<registry> --docker-username=<username> --docker-password=<password>
For example:
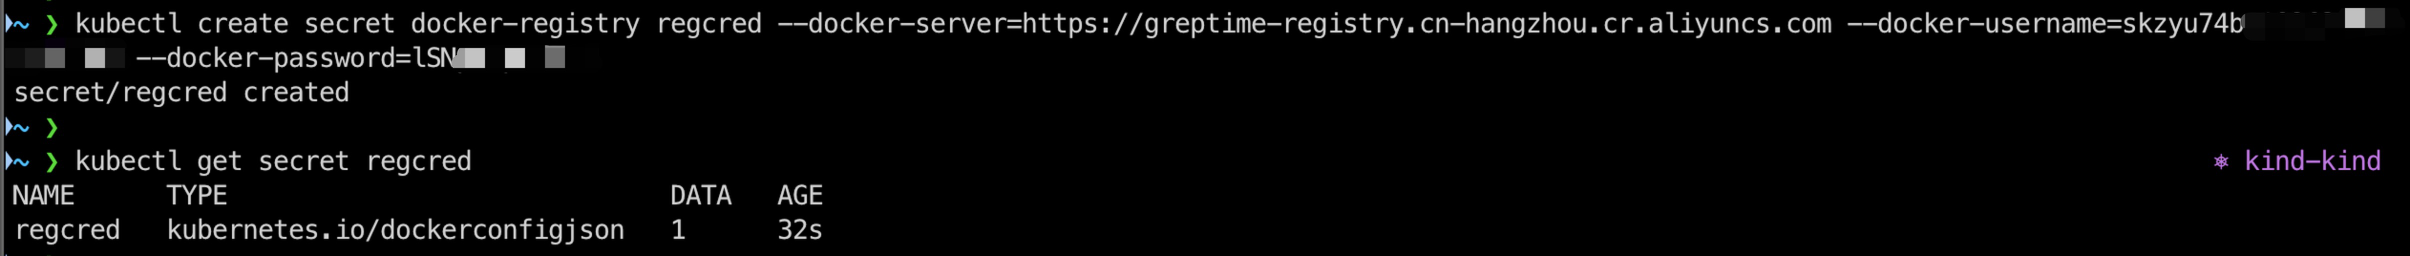
Then add this secret to the helm chart's values.yaml:
image:
  registry: <registry>
  repository: <repository>
  tag: <tag>
  pullSecrets: []
Where <repository> is the part after : in <registry>; <tag> is the unique identifier for the GreptimeDB Enterprise image.
Installation and Startup
Please refer to the Deploy GreptimeDB Cluster on Kubernetes documentation.